We value your privacy
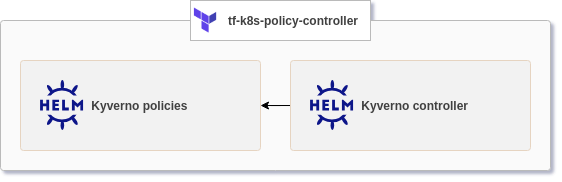
The module deploys Kyverno policy controller and its baseline policies to a Kubernetes cluster
Kyverno is a policy engine that helps to automate security, compliance, best practices validation, and deliver secure self-service.
Key features:
Once you have a Corewide Solutions Portal account, this one-time action will use your browser session to retrieve credentials:
shellterraform login solutions.corewide.com
Initialize mandatory providers:
Copy and paste into your Terraform configuration and insert the variables:
 hclmodule "tf_k8s_policy_controller" {
  source  = "solutions.corewide.com/kubernetes/tf-k8s-policy-controller/helm"
  version = "~> 1.1.0"

  # specify module inputs here or try one of the examples below
  ...
}
Initialize the setup:
shellterraform init
Corewide DevOps team strictly follows Semantic Versioning
Specification
to
provide our clients with products that have predictable upgrades between versions. We
recommend
pinning
patch versions of our modules using pessimistic
constraint operator (~>) to prevent breaking changes during upgrades.
To get new features during the upgrades (without breaking compatibility), use
~> 1.1 and run
terraform init -upgrade
For the safest setup, use strict pinning with version = "1.1.0"
|
Module
65% off
|
€180
|
| TOTAL | €180 |
The module deploys Kyverno policy controller and its baseline policies to a Kubernetes cluster
Kyverno is a policy engine that helps to automate security, compliance, best practices validation, and deliver secure self-service.
Key features:
All notable changes to this project are documented here.
The format is based on Keep a Changelog, and this project adheres to Semantic Versioning.
3.7.1 to 3.9.1) and application (from v1.17.1 to v1.19.1) versionsFirst stable version
Policy controller setup with custom Kyverno's implementation of the Kubernetes Pod Security Standard. Only certain rules from the standard baseline ruleset and a custom rule for Ingress Nginx with a nodeSelector set:
 hclmodule "kyverno" {
  source  = "solutions.corewide.com/kubernetes/tf-k8s-policy-controller/helm"
  version = "~> 1.1"

  name_prefix = "foo"
  namespace   = "kyverno"

  kyverno_pod_policies = {
    security_standard = "custom"

    security_policies = [
      "restrict-sysctls",
      "disallow-host-namespaces",
      "disallow-capabilities",
    ]

    custom_policies = [
      {
        apiVersion = "kyverno.io/v1"
        kind       = "ClusterPolicy"

        metadata = {
          name = "restrict-ingress-classes"

          annotations = {
            "policies.kyverno.io/category"   = "Sample"
            "policies.kyverno.io/minversion" = "1.6.0"
            "policies.kyverno.io/severity"   = "medium"
            "policies.kyverno.io/subject"    = "Ingress"
            "policies.kyverno.io/title"      = "Restrict Ingress Classes"
          }
        }

        spec = {
          validationFailureAction = "Audit"
          background              = true

          rules = [
            {
              name = "validate-ingress"

              match = {
                any = [
                  {
                    resources = {
                      kinds = [
                        "Ingress",
                      ]
                    }
                  },
                ]
              }

              validate = {
                message = "Unknown ingress class."

                pattern = {
                  metadata = {
                    annotations = {
                      "kubernetes.io/ingress.class" = "HAProxy | nginx"
                    }
                  }
                }
              }
            },
          ]
        }
      },
    ]
  }

  node_selector = {
    "cloud.google.com/gke-nodepool" = "maintenance"
  }
}
The basic setup of policy controller along with Kyverno's implementation of the Kubernetes Pod Security Standards with a baseline policy preset:
 hclmodule "kyverno" {
  source  = "solutions.corewide.com/kubernetes/tf-k8s-policy-controller/helm"
  version = "~> 1.1"

  namespace = "kyverno"
}
| Variable | Description | Type | Default | Required | Sensitive |
|---|---|---|---|---|---|
namespace |
The namespace to install resources in | string |
yes | no | |
app_version |
Kyverno controller image version | string |
v1.19.1 |
no | no |
chart_version |
Kyverno controller Helm chart version | string |
3.9.1 |
no | no |
controller_custom_values |
Custom values to pass to the policy controller Helm chart as a block | any |
{} |
no | no |
create_namespace |
Indicates creation of dedicated namespace for the resources | bool |
true |
no | no |
kyverno_pod_policies |
Kyverno policies parameters | object |
{} |
no | no |
kyverno_pod_policies.allow_existing_violations |
Validate already existing resources | bool |
true |
no | no |
kyverno_pod_policies.custom_policies |
Additional custom policies to include | any |
[] |
no | no |
kyverno_pod_policies.include_other_policies |
Additional policies to include from other policy category |
list(string) |
[] |
no | no |
kyverno_pod_policies.include_restricted_policies |
Additional policies to include from restricted policy category |
list(string) |
[] |
no | no |
kyverno_pod_policies.policy_exclude |
Exclude resources from individual policies | any |
{} |
no | no |
kyverno_pod_policies.policy_kind |
Policy kind, set to Policy if you need namespaced policies and not cluster policies. Possible values are: ClusterPolicy and ValidatingPolicy |
string |
ClusterPolicy |
no | no |
kyverno_pod_policies.security_policies |
Policies to include when podSecurityStandard is custom |
list(string) |
[] |
no | no |
kyverno_pod_policies.security_severity |
Pod security standard severity. Possible values are: low, medium, high |
string |
medium |
no | no |
kyverno_pod_policies.security_standard |
Pod security standard profile. Possible values are: baseline, restricted, privileged, and custom |
string |
baseline |
no | no |
name_prefix |
Name prefix for Kyverno resources. Not used if unset | string |
no | no | |
node_selector |
Node selector for Kyverno components | map(string) |
{} |
no | no |
| Dependency | Version | Kind |
|---|---|---|
terraform |
>= 1.3 |
CLI |
hashicorp/helm |
~> 3.1 |
provider |
hashicorp/kubernetes |
~> 3.0 |
provider |
These components are included as is under the terms of their corresponding licenses.
| Component | License |
|---|---|
| Kyverno | Apache 2.0 |
| Kyverno policies | Apache 2.0 |