We value your privacy
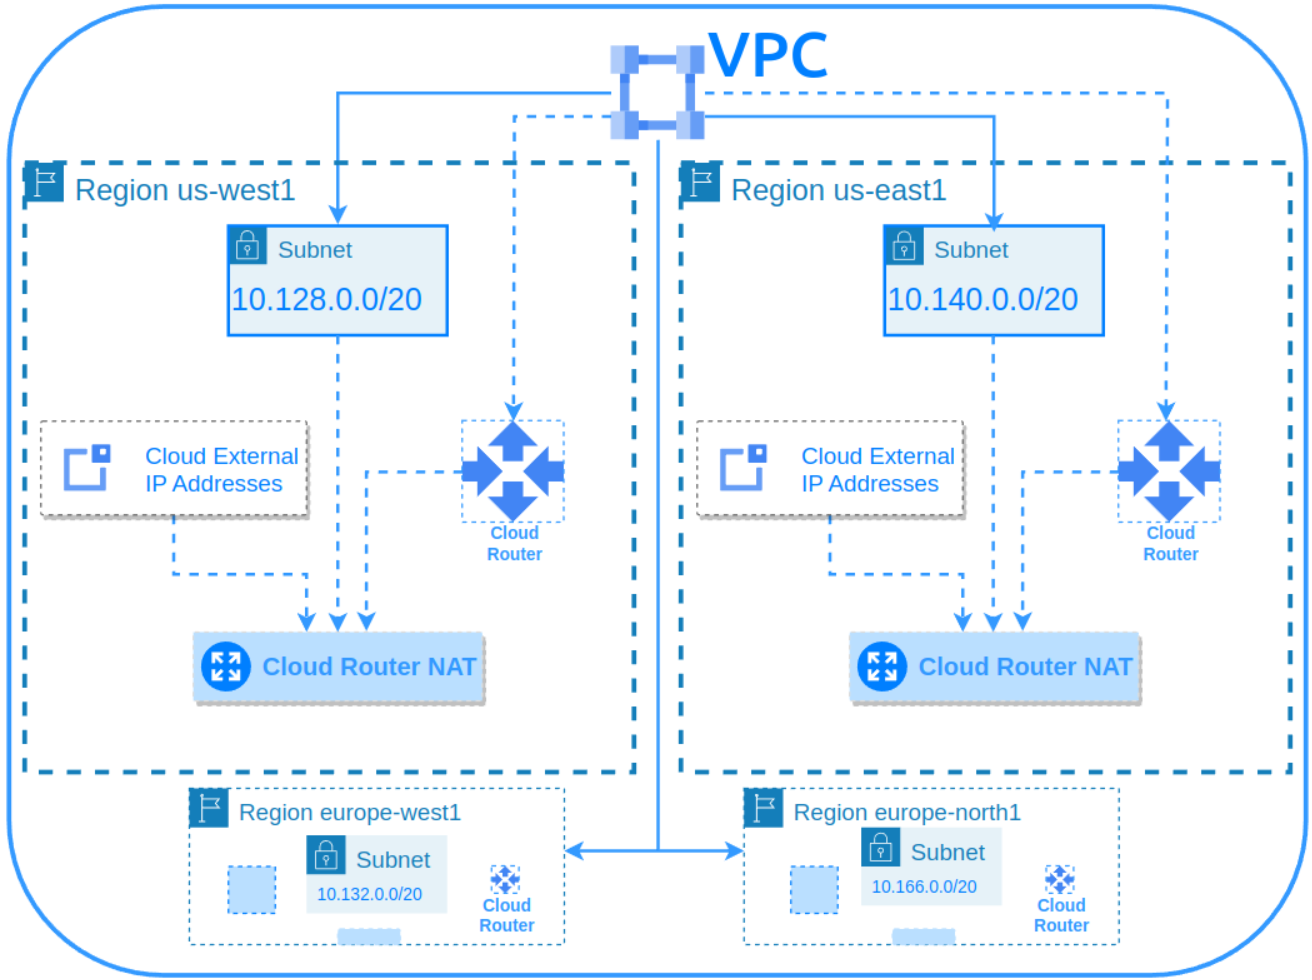
The module creates a set of resources and configures a secure multi-region/regional GCP VPC. The configuration includes subnets with Cloud NAT and external static IP address(es) in the specified region(s). Optional Private Google Access can also be enabled.
Once you have a Corewide Solutions Portal account, this one-time action will use your browser session to retrieve credentials:
shellterraform login solutions.corewide.com
Initialize mandatory providers:
Copy and paste into your Terraform configuration and insert the variables:
 hclmodule "tf_gcp_vpc" {
  source  = "solutions.corewide.com/google-cloud/tf-gcp-vpc/google"
  version = "~> 2.2.0"

  # specify module inputs here or try one of the examples below
  ...
}
Initialize the setup:
shellterraform init
Corewide DevOps team strictly follows Semantic Versioning
Specification
to
provide our clients with products that have predictable upgrades between versions. We
recommend
pinning
patch versions of our modules using pessimistic
constraint operator (~>) to prevent breaking changes during upgrades.
To get new features during the upgrades (without breaking compatibility), use
~> 2.2 and run
terraform init -upgrade
For the safest setup, use strict pinning with version = "2.2.0"
|
Module
10% off
|
€410
|
| TOTAL | €410 |
The module creates a set of resources and configures a secure multi-region/regional GCP VPC. The configuration includes subnets with Cloud NAT and external static IP address(es) in the specified region(s). Optional Private Google Access can also be enabled.
All notable changes to this project are documented here.
The format is based on Keep a Changelog, and this project adheres to Semantic Versioning.
enable_dynamic_port_allocation sub-parameter of the subnets variable to enable dynamic port allocation with default valuesnat_ips sub-parameter of the subnets variable to set additional IP addresses to the Cloud NAT gatewayrouter_nat_logs sub-parameter of the subnets variable to enable logging and configure log filters for a specific Cloud NAT gatewayrouter_nat_logs_enabled variable in favour of subnets.router_nat_logs and will be deleted in v3.0project_id variable7.0(Last version compatible with GCP Terraform provider v6.0)
First stable version
v1.x to v2.xModule from v2.0 has changed GCP provider version which isn't compatible with an old version. After the module version is upgraded, re-init module to upgrade GCP provider version.
Upgrade GCP provider version on project level to ~> 7.0:
 hclterraform {
  required_providers {
    google = {
      source  = "hashicorp/google"
      version = "~> 7.0"
    }
  }
}
Upgrade project dependencies:
bashterraform init --upgrade
In this example, module creates two subnets in different regions using only mandatory values:
 hclmodule "vpc" {
  source  = "solutions.corewide.com/google-cloud/tf-gcp-vpc/google"
  version = "~> 2.2"

  name_prefix = "project-name"

  subnets = {
    database = {
      cidr_block = "10.0.0.0/8"
      region     = "us-west1"
    }

    application = {
      cidr_block = "11.0.0.0/8"
      region     = "us-east1"
    }
  }
}
In this setup, module creates three subnets with configured NAT, private GCP access, regional routes, explicitly specified project ID, and for application subnets, enables dynamic port allocation, router NAT logs, and extra IP addresses for the application gateway:
 hclmodule "vpc" {
  source  = "solutions.corewide.com/google-cloud/tf-gcp-vpc/google"
  version = "~> 2.2"

  name_prefix  = "project-name"
  project_id   = "foo"
  routing_mode = "REGIONAL"

  subnets = {
    database = {
      cidr_block = "11.0.0.0/8"
      region     = "us-west1"
    }

    application = {
      private_access_enabled         = true
      enable_dynamic_port_allocation = true
      cidr_block                     = "12.0.0.0/8"
      region                         = "us-east1"
      nat_ips                        = [google_compute_address.extra_application_nat.self_link]

      router_nat_logs = {
        enable = true
        filter = "ERRORS_ONLY"
      }
    }

    test = {
      private_access_enabled = true
      cidr_block             = "12.0.0.0/8"
      region                 = "us-central1"
    }
  }
}
| Variable | Description | Type | Default | Required | Sensitive |
|---|---|---|---|---|---|
name_prefix |
Naming prefix for all the resources created by the module | string |
yes | no | |
subnets |
The map of specific definitions for the subnets creation | map(object) |
yes | no | |
subnets[<key>] |
subnet name | string |
yes | no | |
project_id |
GCP project ID to manage resources in. If it is not provided, the provider project is used | string |
no | no | |
router_nat_logs_enabled |
Enable logging for NAT structure | bool |
true |
no | no |
routing_mode |
Network-wide routing mode to use | string |
GLOBAL |
no | no |
subnets.router_nat_logs |
Configure logging for Cloud NAT gateway | object |
no | no | |
subnets.router_nat_logs.enable |
Enable logging for Cloud NAT gateway | bool |
false |
no | no |
subnets.router_nat_logs.filter |
Cloud NAT flow logs | string |
ALL |
no | no |
subnets[<key>].cidr_block |
The range of internal addresses that are owned by the subnet | string |
yes | no | |
subnets[<key>].enable_dynamic_port_allocation |
Enable dynamic port allocation for VM from this NAT | bool |
false |
no | no |
subnets[<key>].nat_ips |
Additional GCP IP addresses self_link for the Cloud NAT gateway configuration |
list(string) |
[] |
no | no |
subnets[<key>].private_access_enabled |
Specifies whether VMs in this subnet can access Google APIs and services by using Private Google Access without external IP addresses | bool |
false |
no | no |
subnets[<key>].region |
The GCP region for the subnet and related resources | string |
yes | no |
| Output | Description | Type | Sensitive |
|---|---|---|---|
subnets |
Contains attributes of created subnets | resource |
no |
vpc |
Contains attributes of google_network resource |
resource |
no |
| Dependency | Version | Kind |
|---|---|---|
terraform |
>= 1.3 |
CLI |
hashicorp/google |
~> 7.0 |
provider |