We value your privacy
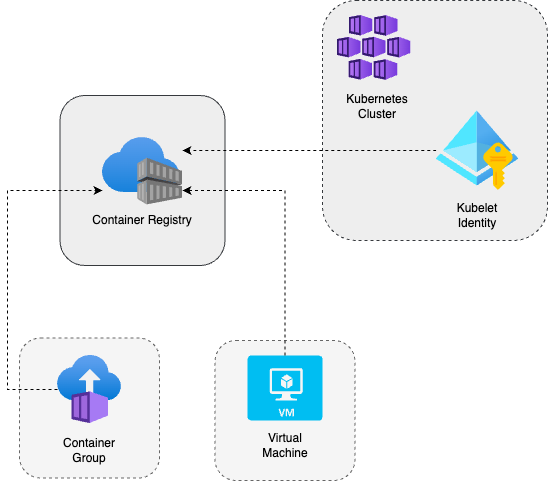
Module manages an Azure Container Registry (creates a new one or manages an existing one), and optionally provides role-assigned registry authorization to Azure resources based on their Principal ID, i.e. Azure Kubernetes Service cluster, Container Instances, managed Virtual Machines, etc.
Once you have a Corewide Solutions Portal account, this one-time action will use your browser session to retrieve credentials:
shellterraform login solutions.corewide.com
Initialize mandatory providers:
Copy and paste into your Terraform configuration and insert the variables:
 hclmodule "tf_azure_acr" {
  source  = "solutions.corewide.com/azure/tf-azure-acr/azurerm"
  version = "~> 1.0.0"

  # specify module inputs here or try one of the examples below
  ...
}
Initialize the setup:
shellterraform init
Corewide DevOps team strictly follows Semantic Versioning
Specification
to
provide our clients with products that have predictable upgrades between versions. We
recommend
pinning
patch versions of our modules using pessimistic
constraint operator (~>) to prevent breaking changes during upgrades.
To get new features during the upgrades (without breaking compatibility), use
~> 1.0 and run
terraform init -upgrade
For the safest setup, use strict pinning with version = "1.0.0"
|
Module
55% off
|
$247
|
| TOTAL | $247 |
Module manages an Azure Container Registry (creates a new one or manages an existing one), and optionally provides role-assigned registry authorization to Azure resources based on their Principal ID, i.e. Azure Kubernetes Service cluster, Container Instances, managed Virtual Machines, etc.
All notable changes to this project are documented here.
The format is based on Keep a Changelog, and this project adheres to Semantic Versioning.
5.0(Last version compatible with the Azure Terraform provider version 4.0)
4.574.2(Last version compatible with the Azure Terraform provider version 3.0)
images_retention variablev1.x to v2.xModule from v2.0 has changed Azure Terraform provider version, which isn't compatible with older versions. After the module version is upgraded, re-init the module to upgrade the provider version. Upgrade the Azure provider version at the project level:
 hclterraform {
  required_providers {
    azurerm = {
      source  = "hashicorp/azurerm"
      version = "~> 4.2"
    }
  }
}
Upgrade project dependencies:
bashterraform init --upgrade
Update the declaration of the module according to the requirements and examples to match the designed configuration, then the configuration can be applied.
Apply the changes to make sure the state of the resources is up-to-date with the new provider version:
bashterraform apply
v2.x to v3.xModule from v3.0 has changed Azure Terraform provider version, which isn't compatible with older versions. After the module version is upgraded, re-init the module to upgrade the provider version. Upgrade the Azure provider version at the project level:
 hclterraform {
  required_providers {
    azurerm = {
      source  = "hashicorp/azurerm"
      version = "~> 5.0"
    }
  }
}
Upgrade project dependencies:
bashterraform init --upgrade
Update the declaration of the module according to the requirements and examples to match the designed configuration, then the configuration can be applied.
Apply the changes to make sure the state of the resources is up-to-date with the new provider version:
bashterraform apply
Create a Container Registry and grant access to managed Kubernetes cluster with read-only permissions:
 hclresource "azurerm_resource_group" "foo" {
  name     = "foo"
  location = "eastus"
}

module "acr" {
  source  = "solutions.corewide.com/azure/tf-azure-acr/azurerm"
  version = "~> 1.0"

  name                = "bar"
  resource_group_name = azurerm_resource_group.foo.name
  region              = azurerm_resource_group.foo.location

  authorize_access = [
    {
      identity = azurerm_kubernetes_cluster.biz.kubelet_identity[0].object_id
    },
  ]
}
Setup for Container Registry management with granting access to several managed Kubernetes clusters in separate workspaces:
 hclresource "azurerm_resource_group" "foo" {
  name     = "foo"
  location = "eastus"
}

module "acr" {
  source  = "solutions.corewide.com/azure/tf-azure-acr/azurerm"
  version = "~> 1.0"

  name                = "bar"
  create              = terraform.workspace == "dev"
  resource_group_name = azurerm_resource_group.foo.name
  region              = azurerm_resource_group.foo.location

  authorize_access = [
    {
      identity    = azurerm_kubernetes_cluster.biz.kubelet_identity[0].object_id
      permissions = terraform.workspace == "dev" ? "rw" : "ro"
    },
  ]
}
Setup for Container Registry management with granting access to managed Kubernetes cluster, Virtual Machine and Container Group:
 hclresource "azurerm_resource_group" "foo" {
  name     = "foo"
  location = "eastus"
}

module "acr" {
  source  = "solutions.corewide.com/azure/tf-azure-acr/azurerm"
  version = "~> 1.0"

  name                = "bar"
  resource_group_name = azurerm_resource_group.foo.name
  region              = azurerm_resource_group.foo.location

  authorize_access = [
    # Authorize AKS cluster with a read-only permissions
    {
      identity = azurerm_kubernetes_cluster.biz.kubelet_identity[0].object_id
    },
    # Authorize Container Group with a read-only permissions
    {
      identity = azurerm_container_group.baz.identity[0].principal_id
    },
    # Authorize VM of managed CI plathorm with read-write permissions
    {
      identity    = azurerm_virtual_machine.ci.identity[0].principal_id
      permissions = "rw"
    }
  ]
}
Create only Container Registry:
 hclresource "azurerm_resource_group" "foo" {
  name     = "foo"
  location = "eastus"
}

module "acr" {
  source  = "solutions.corewide.com/azure/tf-azure-acr/azurerm"
  version = "~> 1.0"

  name                = "bar"
  resource_group_name = azurerm_resource_group.foo.name
  region              = azurerm_resource_group.foo.location
}
| Variable | Description | Type | Default | Required | Sensitive |
|---|---|---|---|---|---|
name |
The name of the Container Registry | string |
yes | no | |
region |
Resource Group location where the Container Registry will be created | string |
yes | no | |
resource_group_name |
The Resource Group Name in which resources will be created | string |
yes | no | |
authorize_access |
Parameters for granting role-assigned registry authorization to Container Registry | list(object) |
[] |
no | no |
authorize_access[*].identity |
Defines an ID of Azure resource identity which should have an access to managed Container Registry (Must be specified if integration with container registry is required) | string |
yes | no | |
authorize_access[*].permissions |
Defines the access level of Azure resource to Container Registry (ro (Read-only) or rw (Read-write)) |
string |
ro |
no | no |
create |
Enable/disable Container Registry creation | bool |
true |
no | no |
sku |
The SKU (purchasable Stock Keeping Unit) name of the Container Registry (Basic, Standard or Premium) |
string |
Basic |
no | no |
| Output | Description | Type | Sensitive |
|---|---|---|---|
registry |
Contains a set of the Container Registry attributes | computed |
no |
| Dependency | Version | Kind |
|---|---|---|
terraform |
>= 1.3 |
CLI |
hashicorp/azurerm |
~> 3.0 |
provider |