We value your privacy
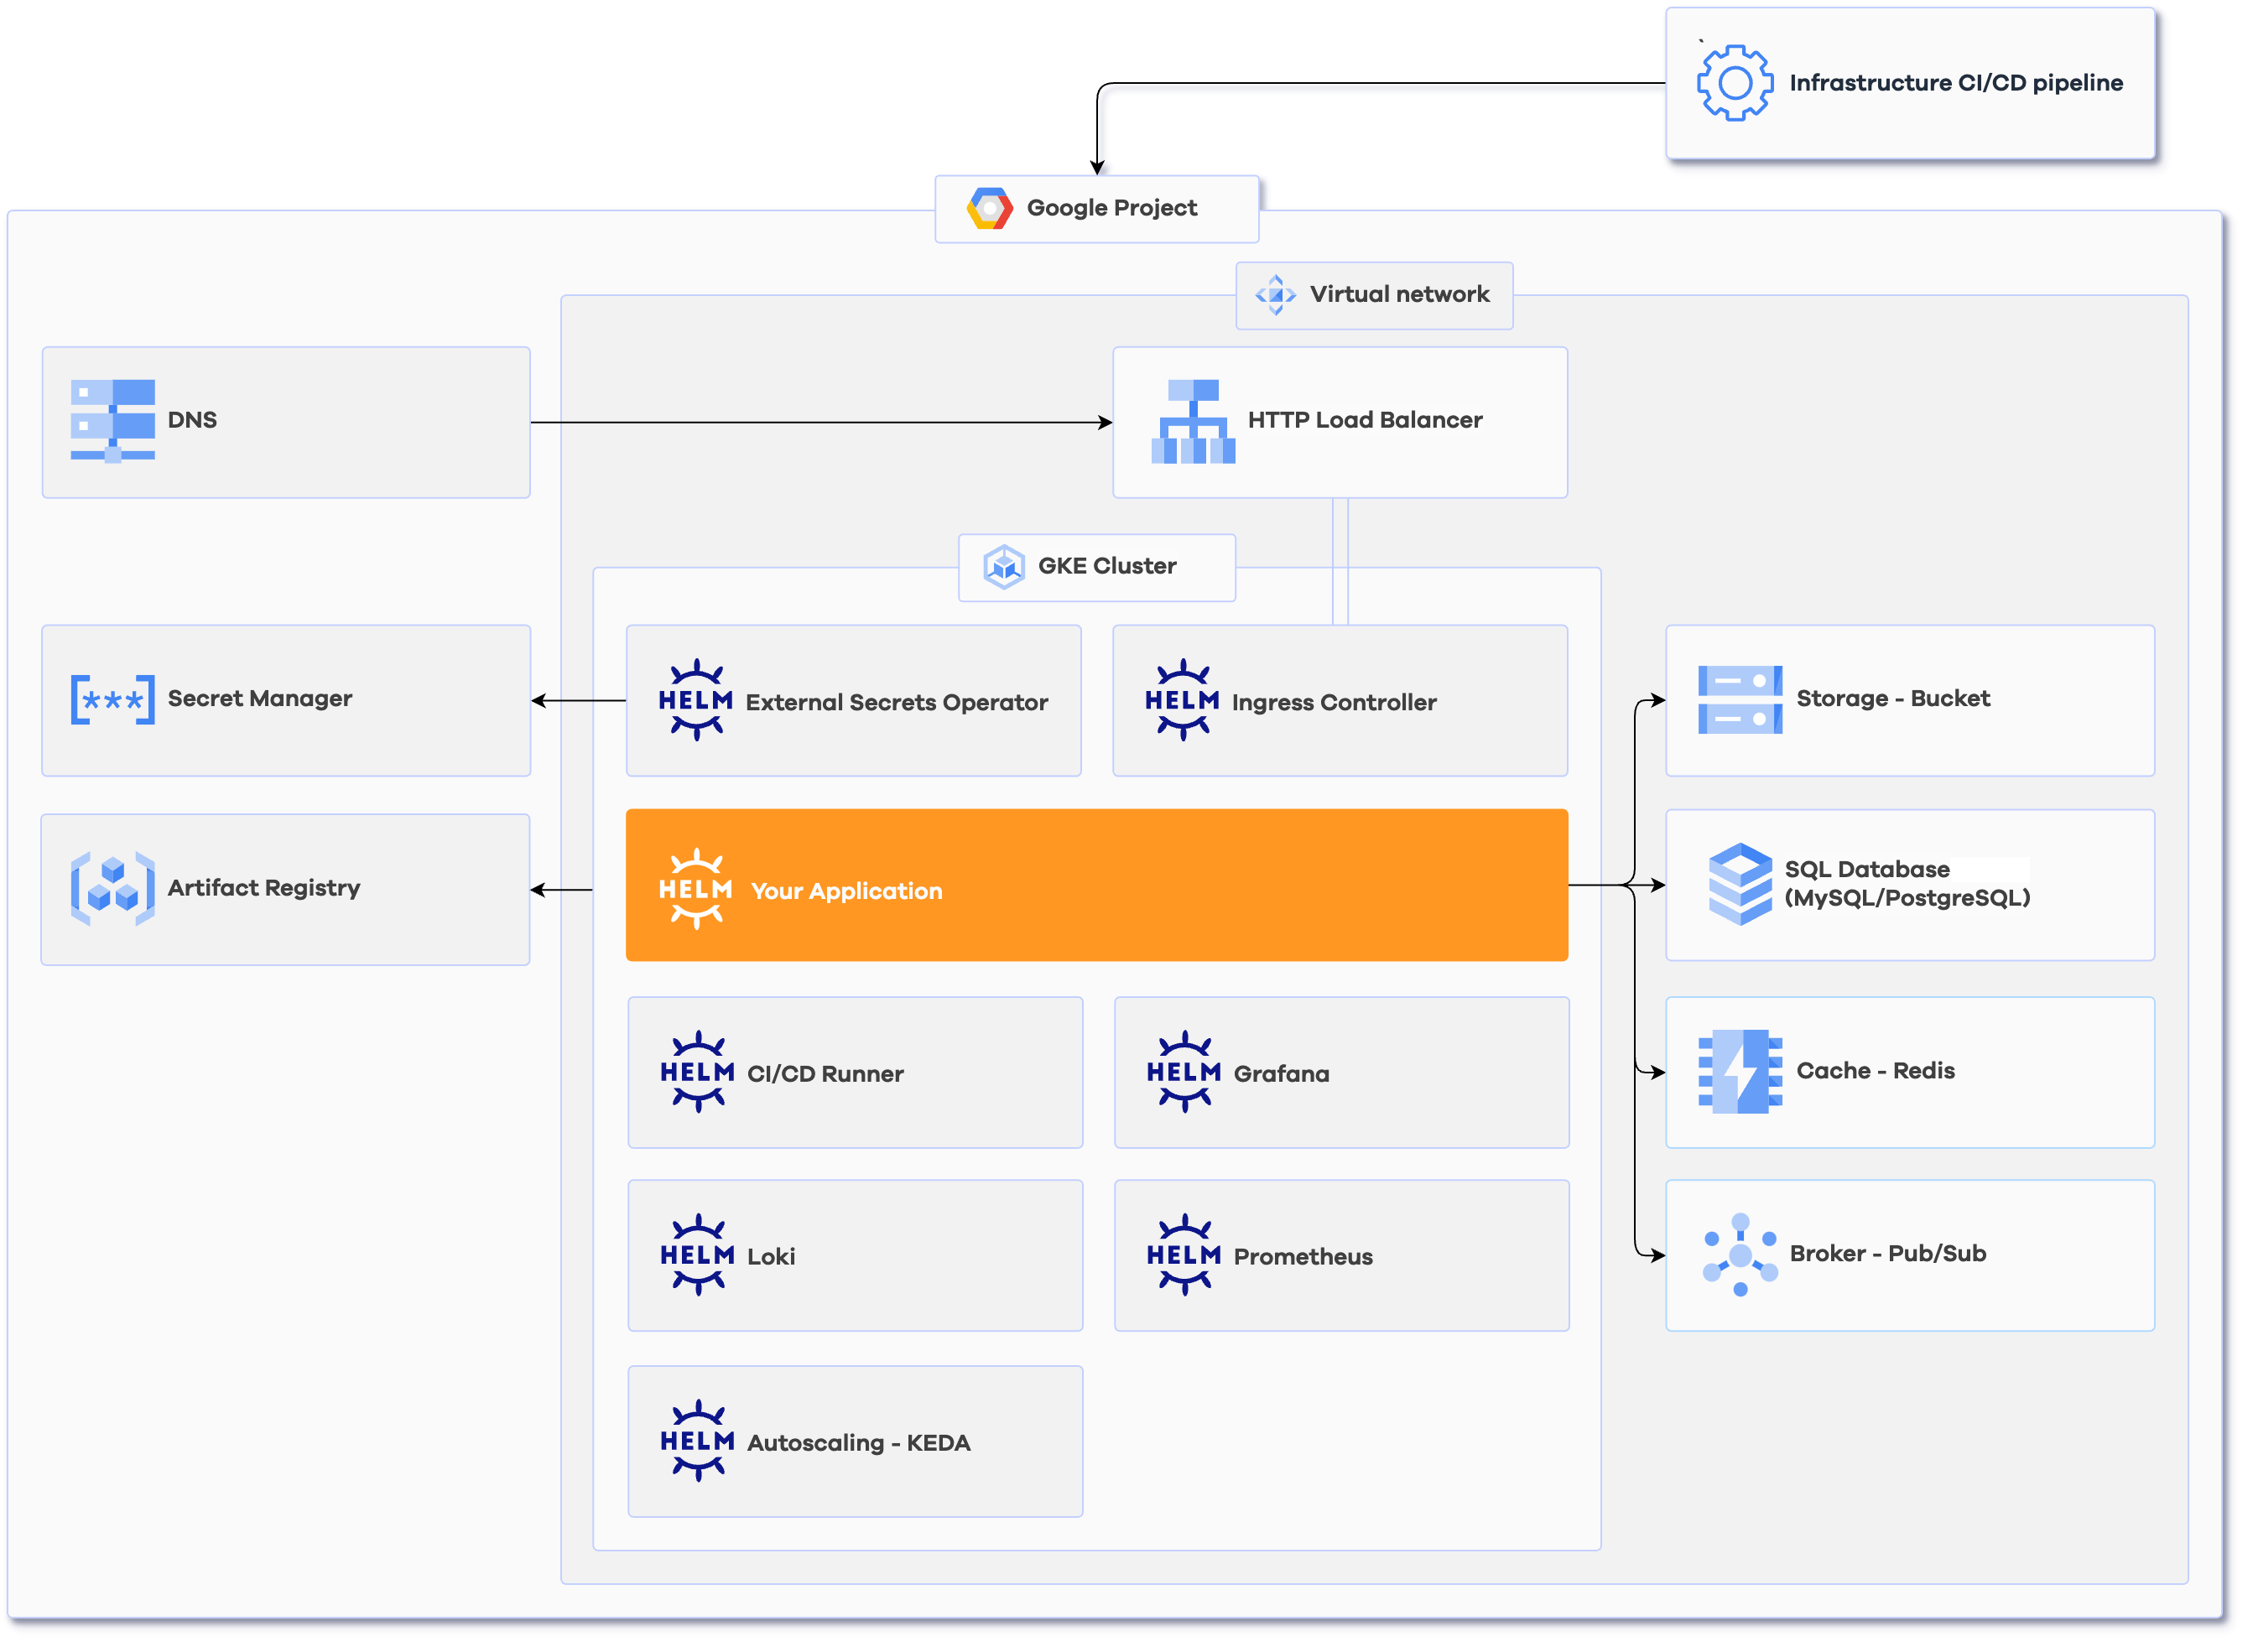
| Components | |
|---|---|
| Artifact Registry in Google Cloud | |
| GCP Kubernetes Cluster | |
| Flexible VPC setup in GCP | |
| Kubernetes ESO for Google Cloud Secret Manager | |
| DNS Management |
GCP DNS
|
| Infrastructure CI/CD pipeline |
GitLab CI
|
| Ingress Controller |
Nginx
|
| Autoscaling | |
| CI/CD Runner |
GitLab Runner
|
| Caching | Memorystore |
| Monitoring | Monitoring Stack |
| Object Storage |
Cloud Storage Buckets
|
| Queue Manager |
Kafka
|
| SQL Database |
Cloud SQL
|
| Helm Chart | |
| Setup by Corewide team | |
| Post-implementation training | |
| 2-week warranty support | |
| Documentation |
Once you have a Corewide Solutions Portal account, this one-time action will use your browser session to retrieve credentials:
shellterraform login solutions.corewide.com
Download Infrasnap archive from My Library page, unpack it to a new directory and initialize a new project there:
 shellcd infrasnap/
git init
git add .
Follow the instructions in README.md:
terraform.tfvars, or using environment variables)
infrasnap.yml parameters based on the reference belowbackend.tf
Initialize the setup, create the environment you configured in infrasnap.yml and
provision
the infrastructure:
 shellterraform init
terraform workspace new <environment_name>
terraform workspace select <environment_name>
terraform apply
| Variable | Description | Type | Default | Required | Sensitive |
|---|---|---|---|---|---|
project_name |
Project name to use for resource naming | string |
yes | no | |
config |
Infrasnap configuration data | any |
{} |
no | no |
config_file |
Path to a YAML file with Infrasnap configuration data | string |
./infrasnap.yml |
no | no |
project_id |
GCP Project ID (can be set as GOOGLE_PROJECT/GOOGLE_CLOUD_PROJECT/GCLOUD_PROJECT environment variables) |
string |
no | no | |
service_account_credentials_file |
Either the path to or the content of a GCP service account key file in JSON format (can be set as GOOGLE_CREDENTIALS/GOOGLE_CLOUD_KEYFILE_JSON/GCLOUD_KEYFILE_JSON environment variables) |
string |
no | no | |
gitlab_runner_authentication_token |
Authentication token for GitLab Runner | string |
yes | yes |
| Variable | Description | Type | Default |
|---|---|---|---|
region |
GCP region to place the resources into | string |
us-east1 |
vpc_cidr_kubernetes |
CIDR block for Kubernetes stack of this environment | string |
10.10.0.0/16 |
vpc_cidr_data |
CIDR block for data stack (databases/caches) of this environment | string |
10.11.0.0/16 |
container_registry_workspace |
Environment where container registry must be created. Leave blank to not create at all | string |
development |
container_registry_repo_max_images |
Number of images stored before cleanup starts | number |
50 |
container_registry_repo_names |
List of container repositories to create | list |
|
k8s_zone |
Region zone index for the zonal cluster. Leave blank to use regional cluster | string |
|
k8s_version |
Kubernetes engine version to deploy the cluster with | string |
1.34 |
k8s_deletion_protection_enabled |
Enables deletion protection of the GKE cluster | bool |
true |
k8s_default_node_pool_node_size |
Machine type to use for all nodes in the default node pool | string |
e2-standard-2 |
k8s_default_node_pool_max_size |
Maximum number of nodes in the default node pool (for autoscaling) | number |
2 |
k8s_node_pools |
List of Kubernetes node pool definitions | list |
|
k8s_node_pools[*].name |
Name of the node pool to create | string |
application |
k8s_node_pools[*].node_size |
Machine type to use for all nodes in this node pool | string |
e2-standard-2 |
k8s_node_pools[*].max_size |
Maximum number of nodes in the node pool (for autoscaling) | number |
3 |
dns_zone_create |
Whether to create DNS zone or use the existing one | bool |
false |
dns_zone |
DNS zone in which to create records, disable to reuse the same zone from another workspace | string |
example.com |
dns_records_k8s |
A list of subdomains that must point at Ingress LoadBalancer | list |
|
dns_records |
List of extra records that do not point at Ingress LoadBalancer. See module_docs for complete reference. Note: when adding CNAME record in the same dns_zone, supply full dns record value e.g. value.dns_zone. |
map |
|
dns_records.test |
Name of the DNS record | map |
|
dns_records.test.type |
Record type (A, AAAA, CNAME, MX, NS, or TXT) |
string |
CNAME |
dns_records.test.value |
List of values for the record | list |
['test.example.com'] |
dns_records.test.ttl |
Time to Live (TTL) of the record in seconds | number |
31 |
dns_records.test.priority |
The priority of the record (only for MX type) |
number |
3600 |
cert_manager_email |
E-mail that Let's Encrypt cluster issuer will use to request certificates | string |
[email protected] |
cicd |
map |
||
cicd.gitlab_url |
GitLab server URL to connect GitLab Runner to | string |
https://gitlab.com |
cicd.node_pool_name |
Name of node pool to place GitLab Runner | string |
maintenance |
cicd.job_node_pool_name |
Name of node pool to place GitLab Runner Jobs | string |
maintenance |
cache_multi_az_enabled |
Indicates whether High Availability is enabled for the main cluster | bool |
true |
cache_shard_count |
Number of Redis cluster shards. Must be greater than 0 | number |
1 |
cache_node_size |
Redis cluster node size. Possible values are: REDIS_SHARED_CORE_NANO, REDIS_HIGHMEM_MEDIUM, REDIS_HIGHMEM_XLARGE, REDIS_STANDARD_SMALL |
string |
REDIS_HIGHMEM_MEDIUM |
cache_node_replica_count |
Count of node replicas per shard. Value must be in 0-2 range | number |
0 |
cache_deletion_protection_enabled |
Indicates whether the main cluster is deletion protected | bool |
true |
cache_traffic_encryption_enabled |
Indicates whether in-transit encryption for the Redis cluster is enabled | bool |
true |
grafana_enabled |
Toggle Grafana installation (must be active only in one workspace) | bool |
true |
grafana_subdomain |
Definition of Grafana subdomain (mon by default) |
string |
mon |
loki_enabled |
Toggle Loki installation | bool |
true |
prometheus_enabled |
Toggle Prometheus installation | bool |
true |
monitoring_stack_node_pool_name |
Name of node pool to place Grafana, Loki and Prometheus pods in | string |
maintenance |
buckets |
Buckets definitions to create | map |
|
buckets.my-bucket |
Bucket name | map |
|
buckets.my-bucket.access_mode |
Cloud Storage bucket access mode. Allowed values: private, public-read |
string |
private |
buckets.my-bucket.versioning |
Enable versioning for the bucket | bool |
false |
kafka_vcpu_count |
Number of vCPU threads to provision for Kafka. Minimal value is 3 |
number |
3 |
kafka_memory_size_gib |
The memory to provision for the cluster (GiB). The value must be between 1 GiB and 8 GiB per one vCPU | number |
3 |
kafka_rebalance_mode |
The rebalance behavior for the cluster. Possible values are: NO_REBALANCE, AUTO_REBALANCE_ON_SCALE_UP |
string |
NO_REBALANCE |
sql_database_engine |
Cloud SQL instance engine | string |
postgres |
sql_database_engine_version |
Cloud SQL instance engine version | string |
16 |
sql_database_machine_size |
Cloud SQL instance machine size | string |
db-f1-micro |
sql_database_edition |
The edition of the database instance, can be enterprise or enterprise_plus |
string |
enterprise |
sql_database_sqlserver_edition |
SQL Server edition. Only applicable for SQL Server. Possible values: standard, enterprise, express, web |
string |
standard |
sql_database_deletion_protection_enabled |
Enables deletion protection of the primary Cloud SQL instance | bool |
true |
sql_database_multi_az_enabled |
Enables High Availability for the primary Cloud SQL instance | bool |
true |
sql_databases_list |
List of databases to create | list |
| Output | Description | Type | Sensitive |
|---|---|---|---|
app_namespace |
Kubernetes namespace to deploy the application to | attribute |
no |
application_secret |
Name of GCP Secret Manager secret for sensitive data of the application. Insert values there manually | attribute |
no |
cluster_connection_cli |
CLI command to connect to the cluster | computed |
no |
container_registries |
GCR repositories to push container images to | computed |
no |
registry_connection_cli |
CLI command to authenticate to the container registry | computed |
no |
name_servers |
Name servers of DNS zone managed in this workspace | attribute |
no |
memorystore_connection_secret_name |
Name of GCP Secret Manager secret with Memorystore connection parameters | attribute |
no |
grafana_admin_credentials |
Contains admin user credentials for Grafana web UI | attribute |
yes |
monitoring_basic_auth_credentials |
Basic auth credentials for Prometheus and Loki endpoints | attribute |
yes |
monitoring_endpoints |
Endpoints of monitoring components | attribute |
no |
bucket_names |
List of bucket names | list(attribute) |
no |
kafka_connection_secret_name |
Name of GCP Secret Manager secret with Kafka connection parameters | attribute |
no |
cloudsql_connection_secret_name |
Name of GCP Secret Manager secret with Cloud SQL connection parameters | attribute |
no |